A protocol, auditor, or OTC counterparty may ask you to prove that you control a Solana address. You can do this without moving funds by signing a message and having the counterparty verify its signature.
Message signing is off-chain: it does not create a Solana transaction or incur a network fee. A valid signature confirms that the message was signed using the key associated with the address.
This guide uses Fordefi to sign the message and Solscan’s Verified Signature tool to verify it. You can publish the result on Solscan and share a URL, or send the verification details directly to the verifier.
- Create an API User with the Trader role, an access token, and request signing. Learn more.
- Set up and run an API Signer, or ensure your existing API Signer is running. Learn more.
- Choose the Solana vault address you need to prove ownership of.
- Agree on the message with the verifier. Include the purpose of the request and, ideally, a unique reference or date so the proof is tied to this request.
In the Solana personal-message signing example, replace the example
MESSAGEvalue with the exact message you agreed on. Configure the example for the Solana vault you want to prove ownership of, then run it.Once signing is complete, copy these three values from the terminal output:
- Signed message
- Signer wallet
- Signature (base58)
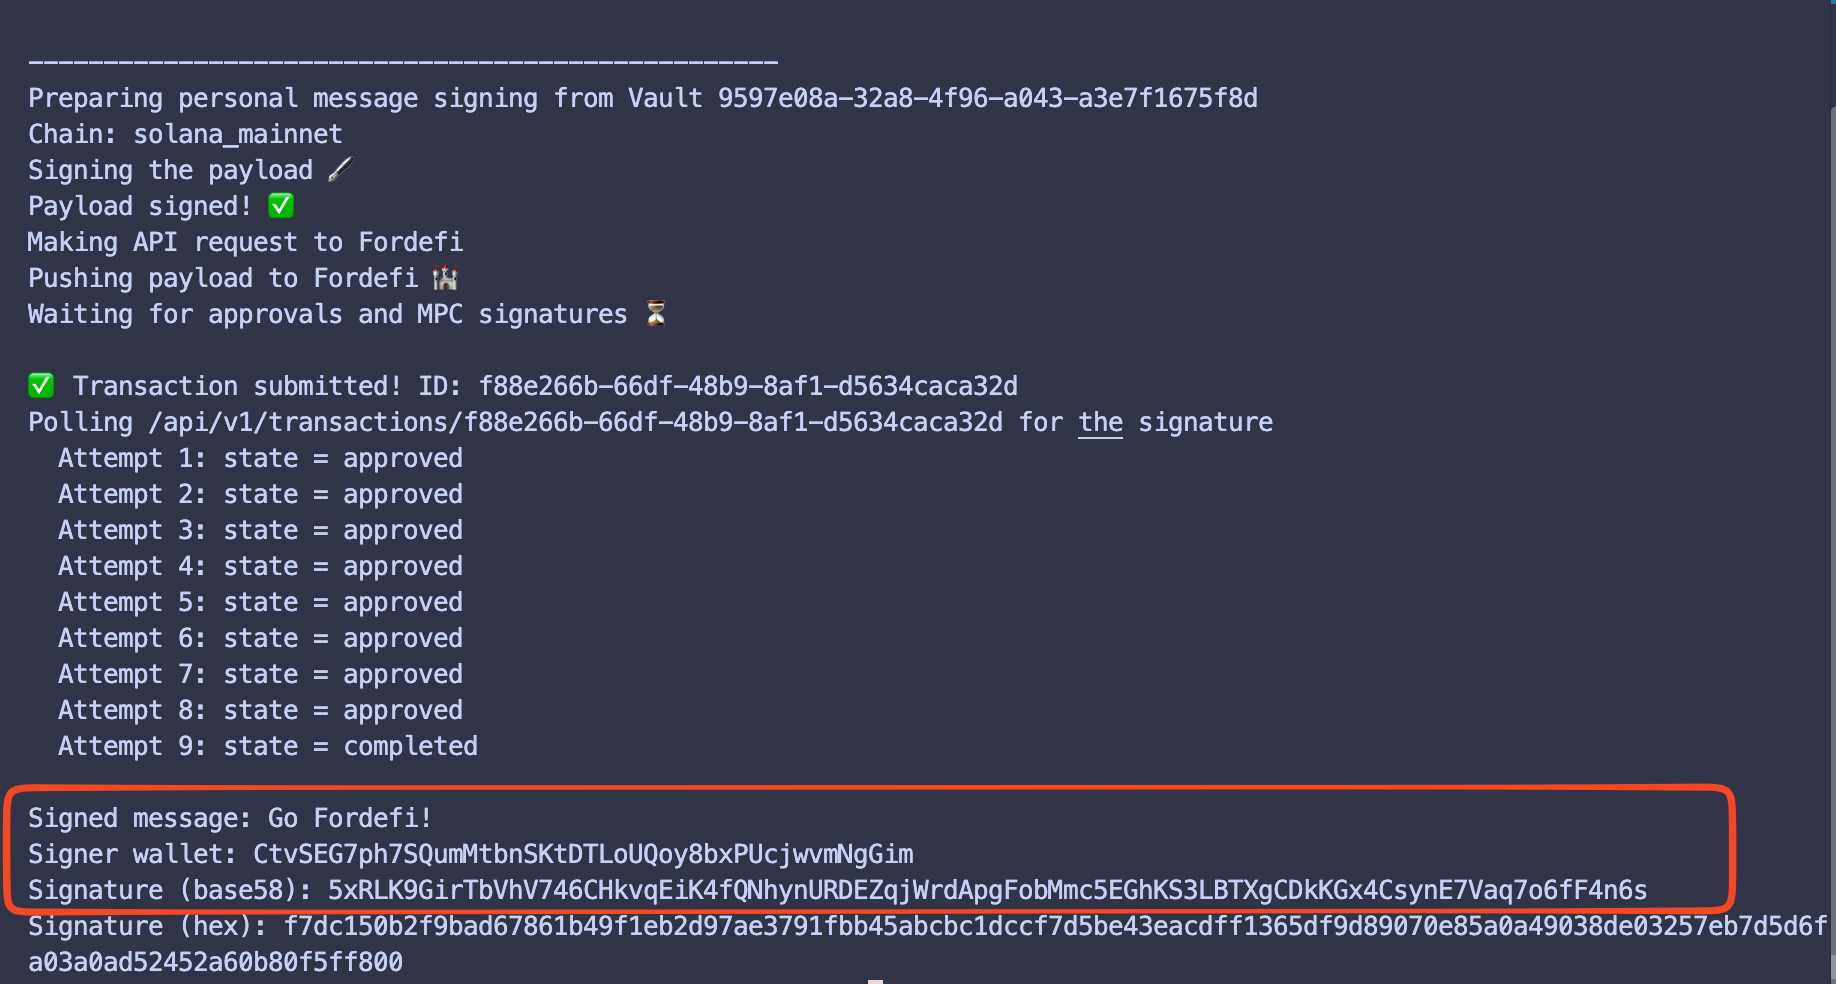
Use the Signature (base58) value for Solscan. It is an off-chain message signature, not a Solana transaction hash.
Open Solscan’s Verified Signature tool and select Verify Signature.
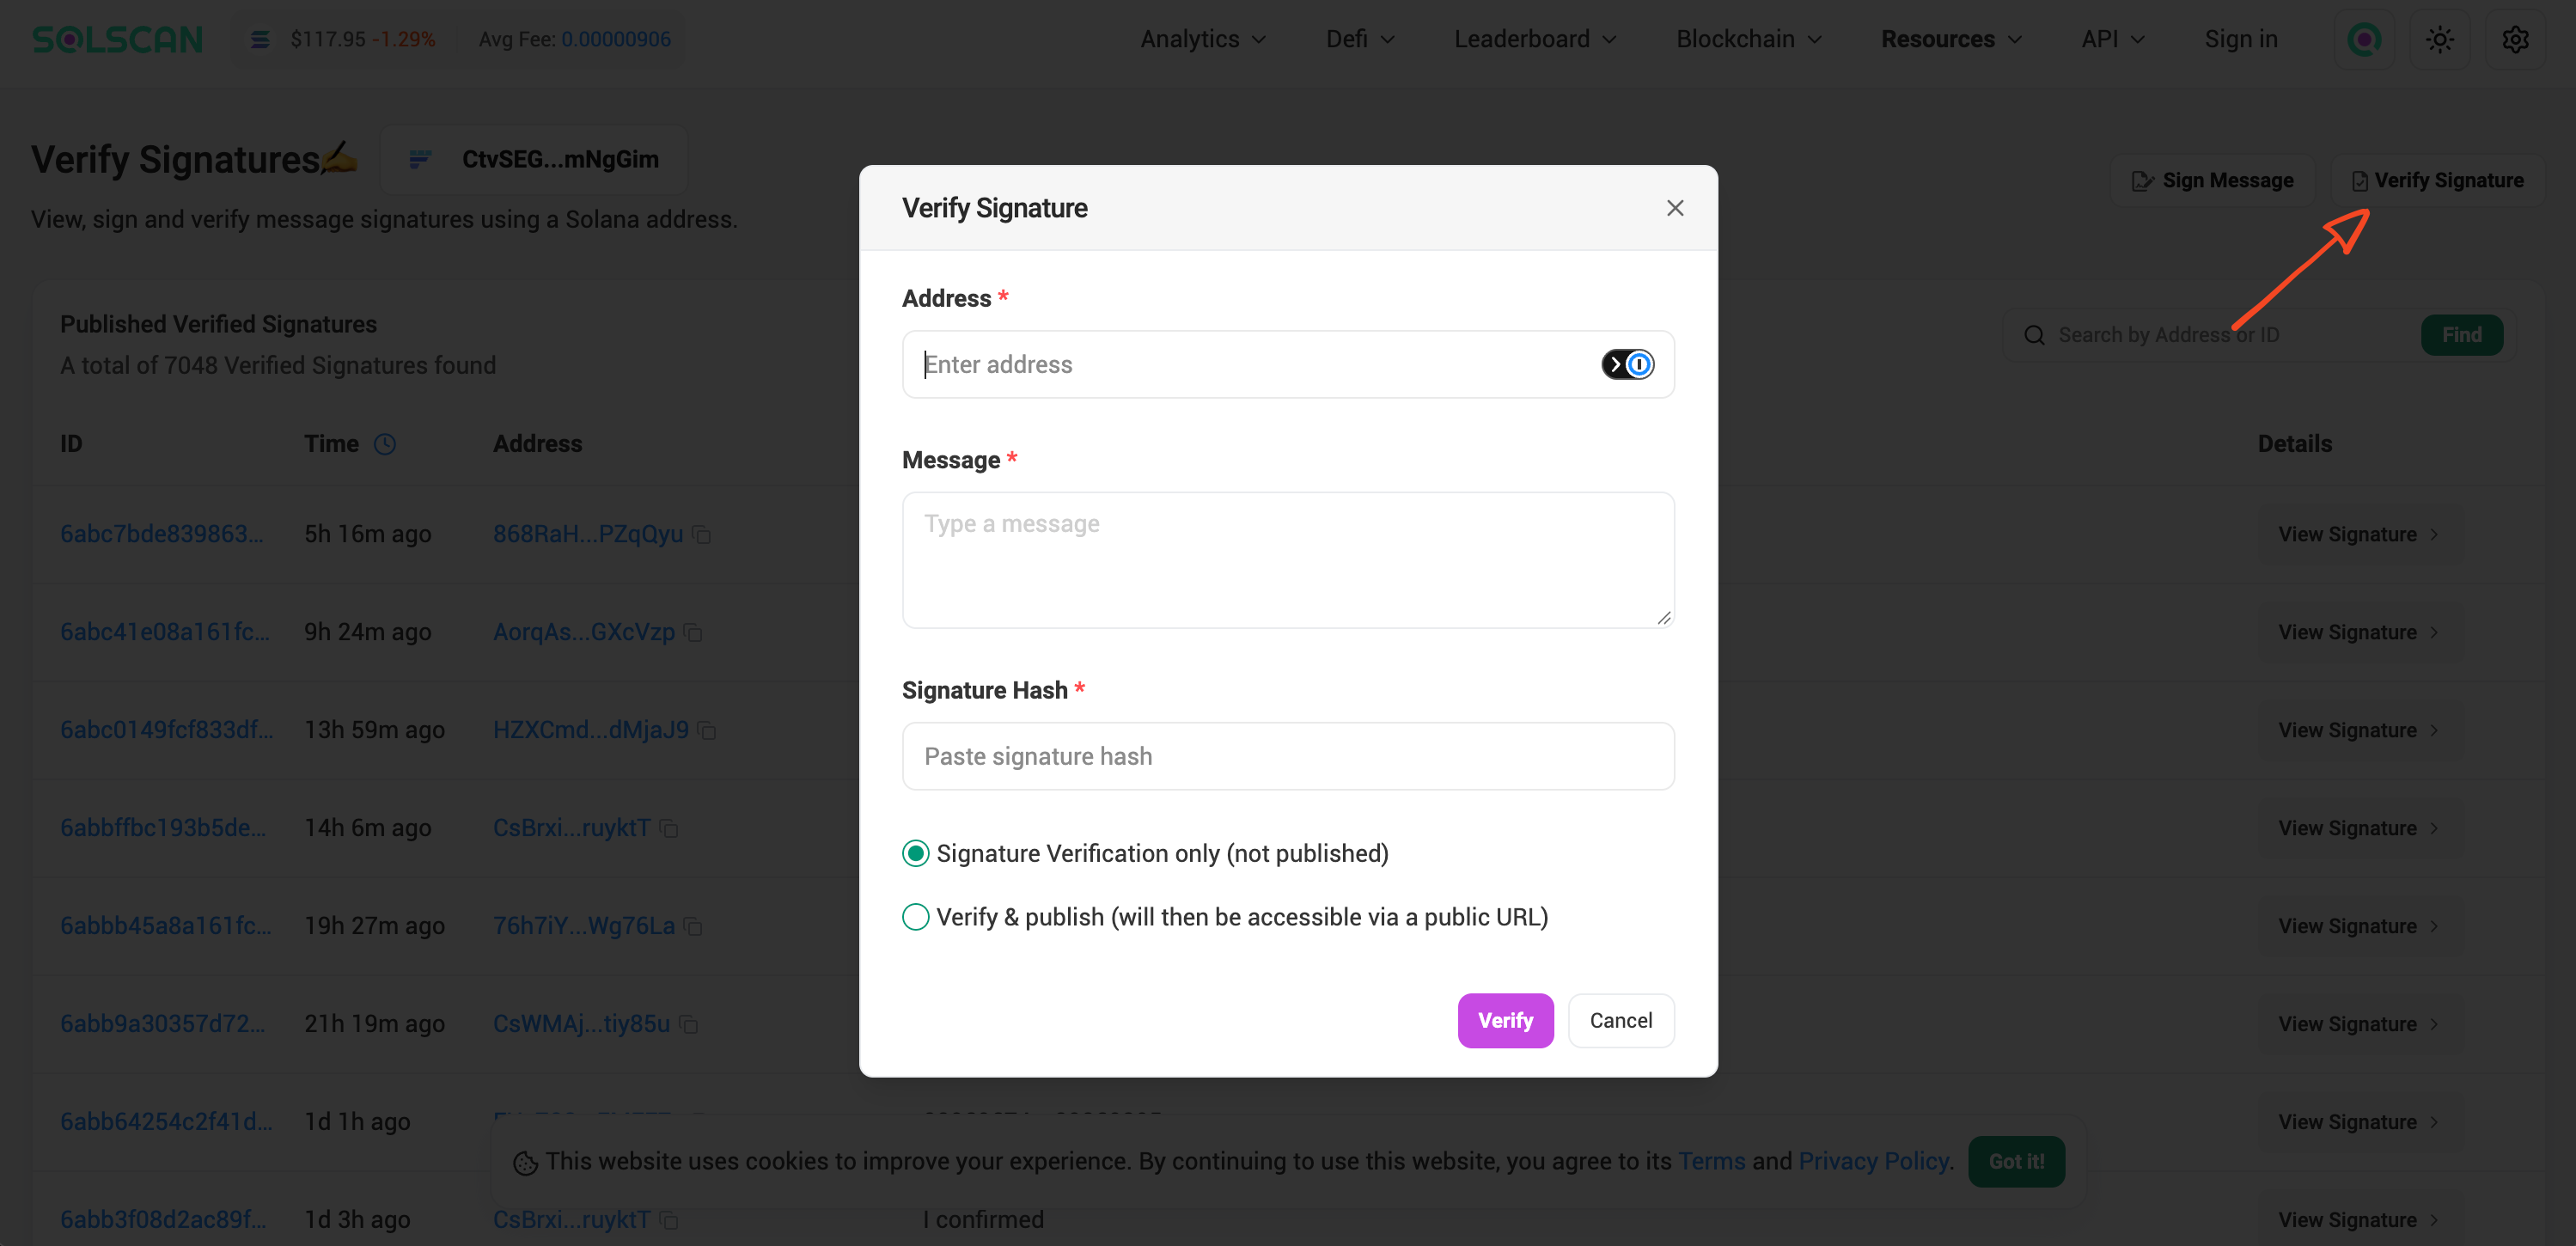
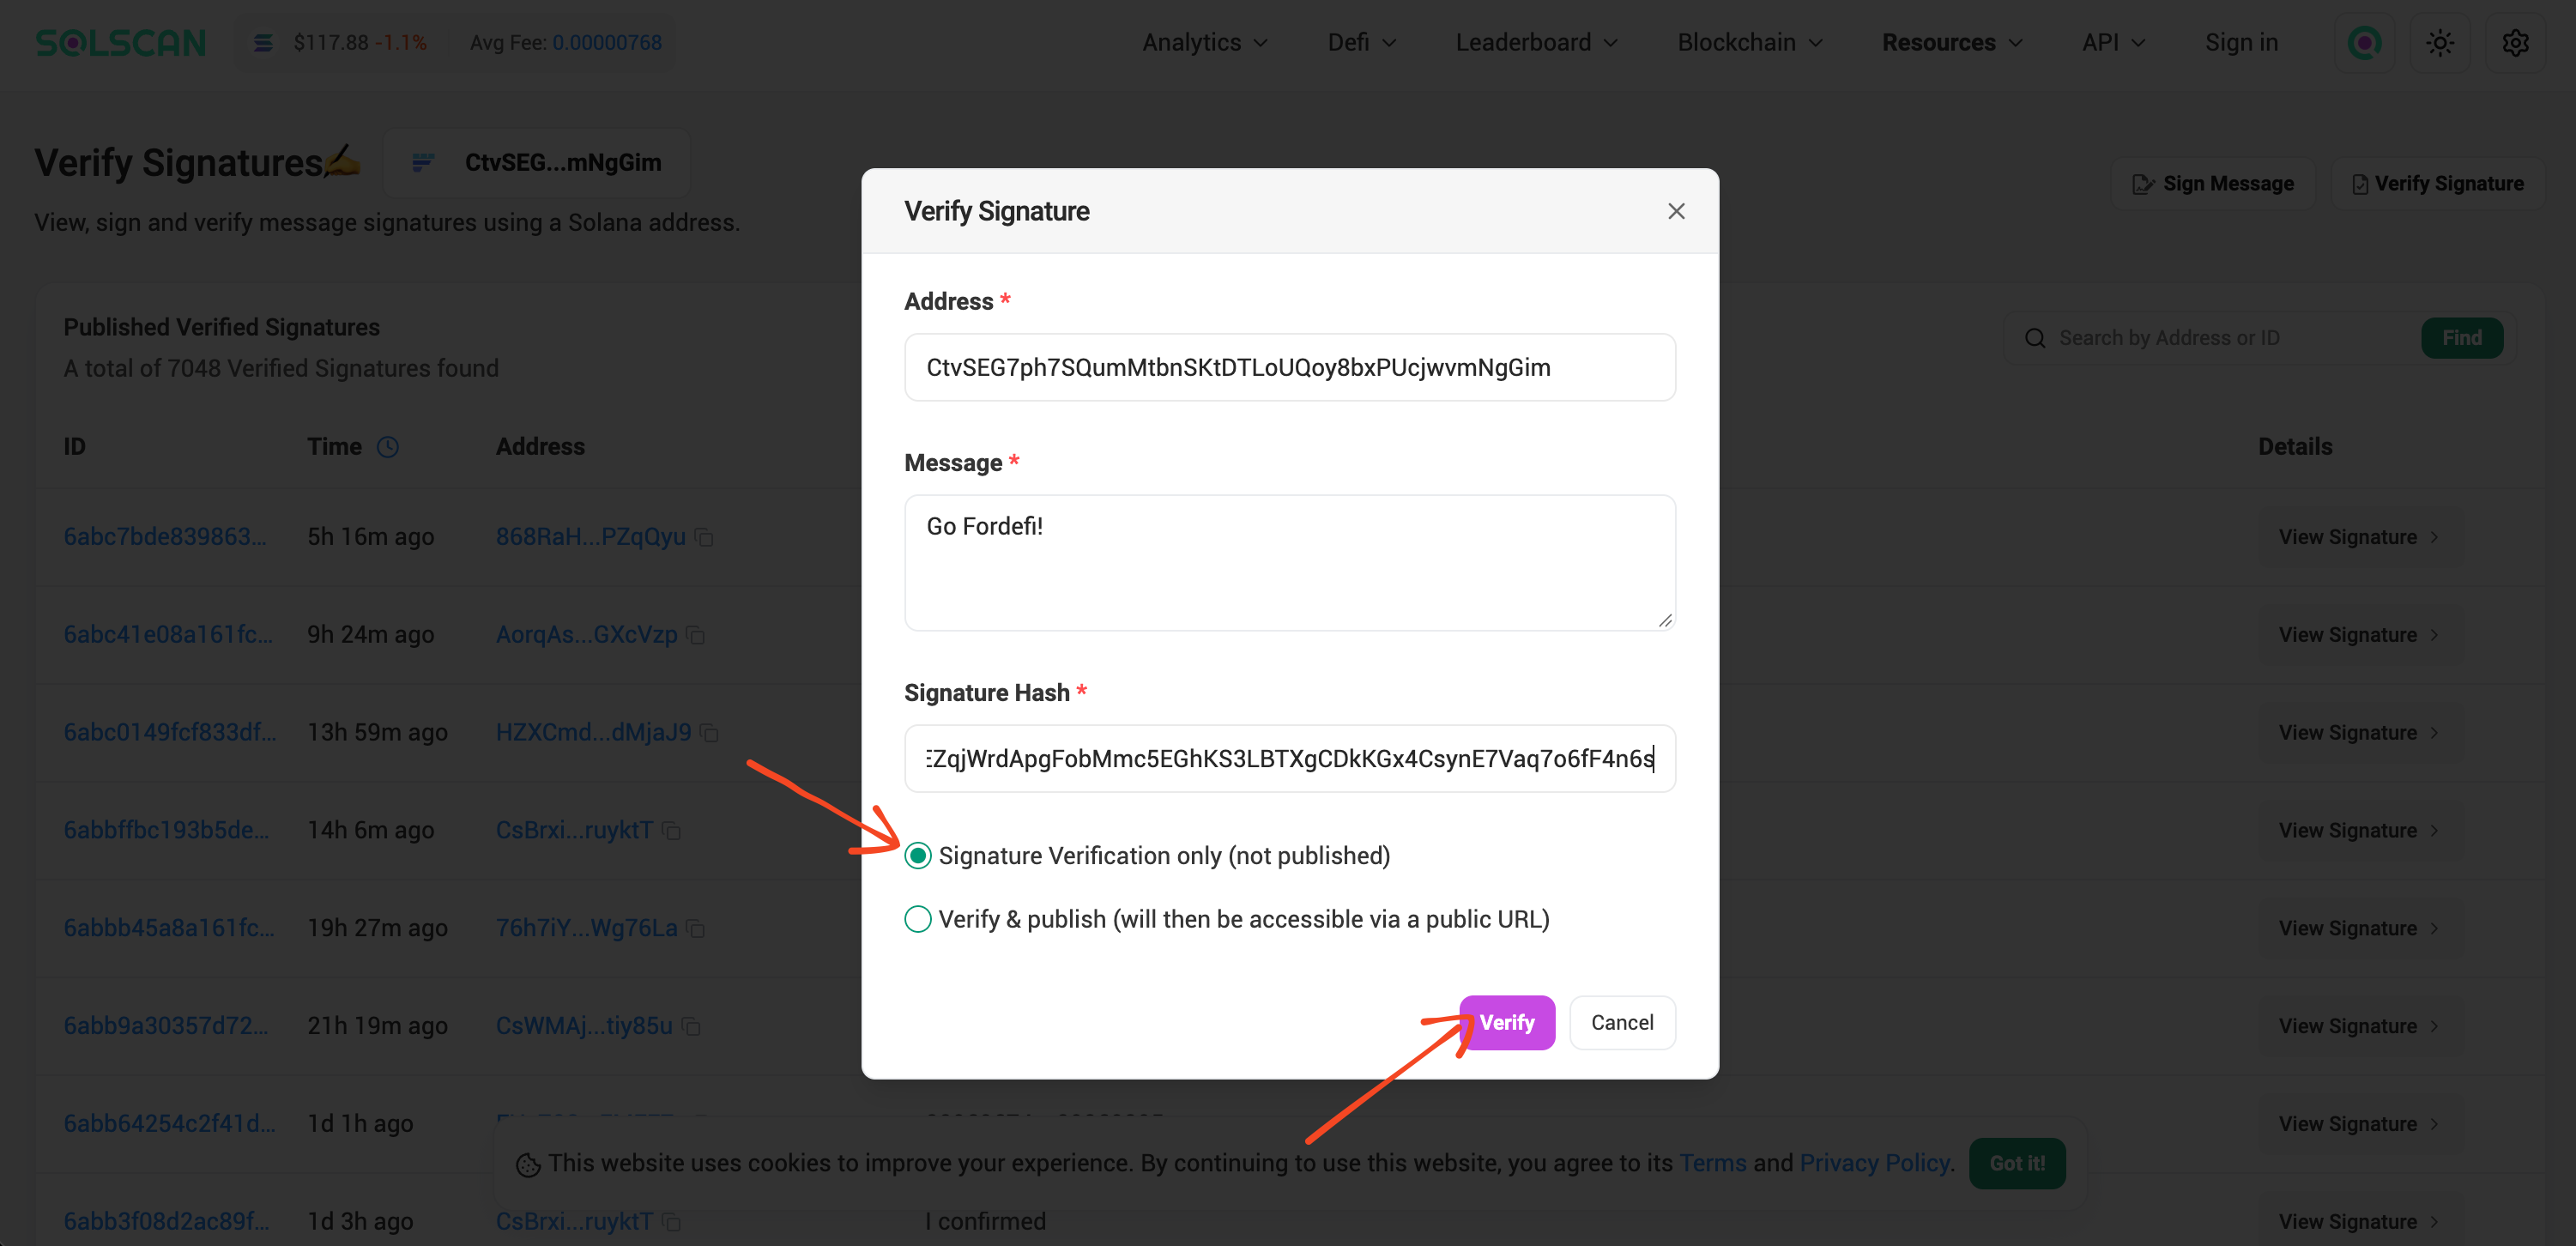
Enter the values from the Fordefi script:
Solscan field Fordefi script output Address Signer wallet Message Signed message Signature Hash Signature (base58) Copy the message exactly, including capitalization, spaces, and line breaks.
Click Verify. Solscan should confirm that the signature is valid for the address and message.
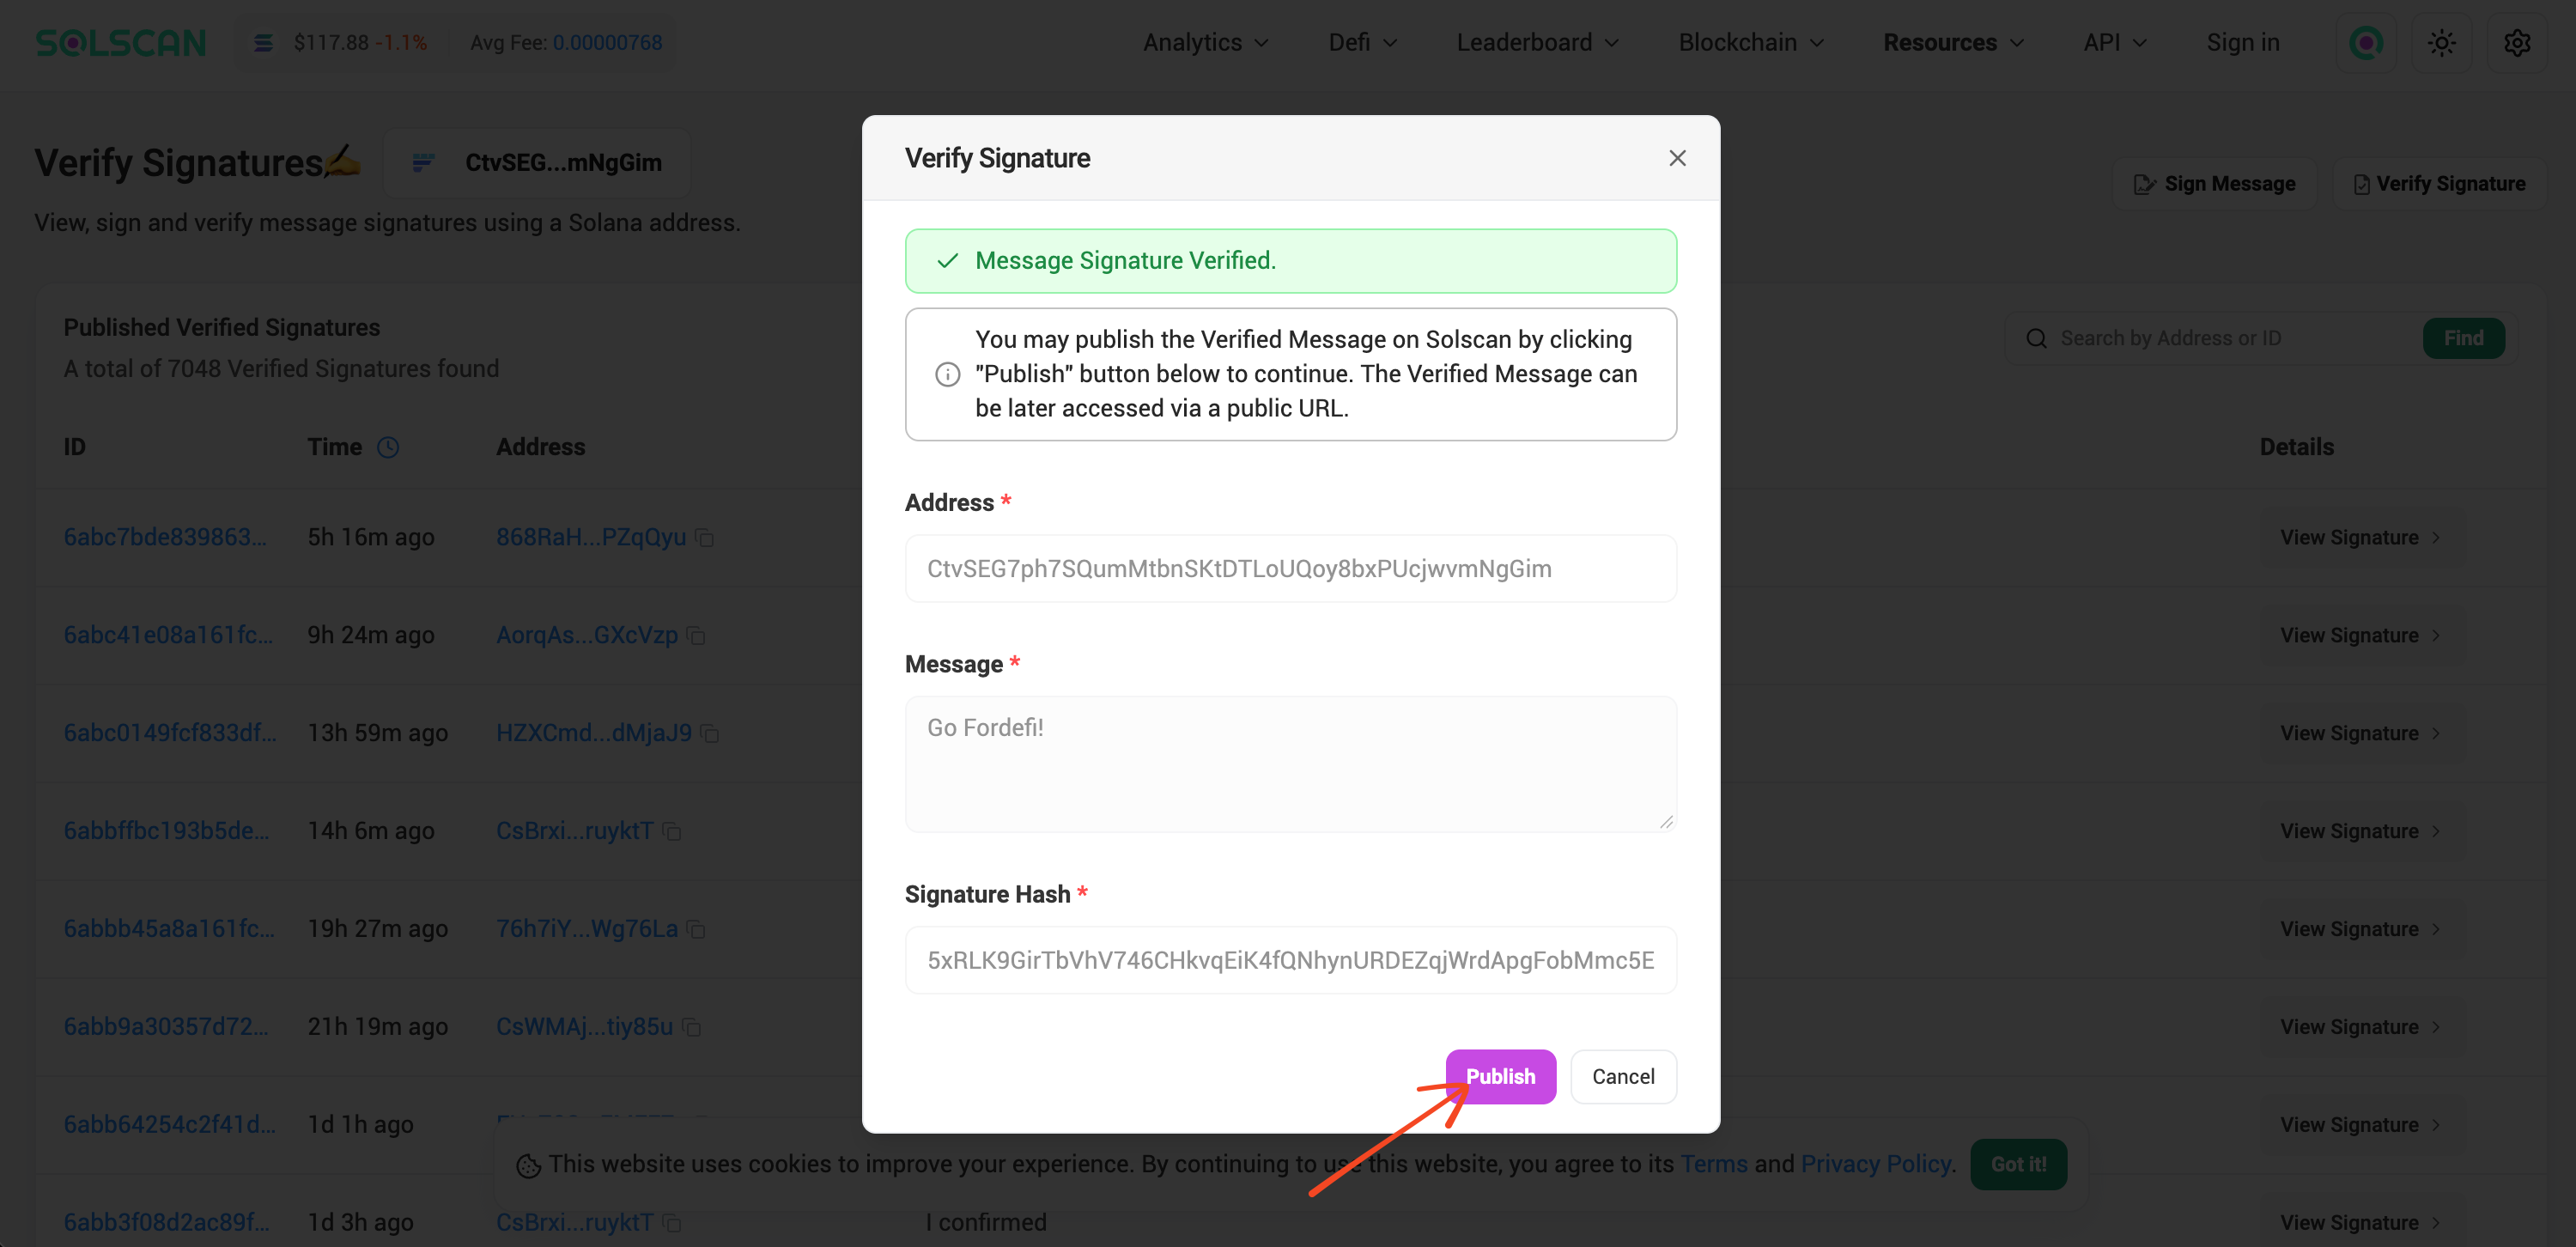
Select Solscan’s Publish option after verifying the signature, then share the resulting public URL with the verifier.
Publishing makes the message publicly visible on Solscan. Do not publish a message containing personal or sensitive information.
If you do not want to publish the message, send the verifier these three values directly:
- The Signer wallet address
- The exact Signed message
- The Signature (base58)
The verifier can enter them into Solscan’s Verify Signature form to confirm that the address signed the message.